


2022 Valid Identity-and-Access-Management-Designer Real Exam Questions (Updated) 100% Dumps & Practice Exam
[UPDATED 2022] Salesforce Identity-and-Access-Management-Designer Questions Prepare with Free Demo of PDF
NEW QUESTION 32
Universal Containers (UC) has an existing web application that it would like to access from Salesforce without requiring users to re-authenticate. The web application is owned UC and the UC team that is responsible for it is willing to add new javascript code and/or libraries to the application. What implementation should an Architect recommend to UC?
- A. Create a Canvas app and use Signed Requests to authenticate the users.
- B. Rewrite the web application as a set of Visualforce pages and Apex code.
- C. Configure the web application as an item in the Salesforce App Launcher.
- D. Add the web application as a ConnectedApp using OAuth User-Agent flow.
Answer: A
NEW QUESTION 33
The security team at Universal containers(UC) has identified exporting reports as a high-risk action and would like to require users to be logged into salesforce with their active directory (AD) credentials when doing so. For all other uses of Salesforce, Users should be allowed to use AD credentials or salesforce credentials. What solution should be recommended to prevent exporting reports except when logged in using AD credentials while maintaining the ability to view reports when logged in with salesforce credentials?
- A. Use SAML Federated Authentication, treat SAML sessions as high assurance, and raise the session level required for exporting reports.
- B. Use SAML Federated Authentication with a login flow to dynamically add or remove a permission set that grants the export reports permission.
- C. Use SAML Federated Authentication and Custom SAML jit provisioning to dynamically add or remove a permission set that grants the Export Reports permission.
- D. Use SAML Federated Authentication and block access to reports when accesses through a standard assurance session.
Answer: D
NEW QUESTION 34
Universal Containers (UC) has a custom, internal-only, mobile billing application for users who are commonly out of the office. The app is configured as a Connected App in Salesforce. Due to the nature of this app, UC would like to take the appropriate measures to properly secure access to the app.
Which two solutions should be recommended? (Choose two.)
- A. Set Login IP Ranges to the internal network for all of the app users' Profiles.
- B. Require High Assurance sessions in order to use the Connected App.
- C. Disallow the use of Single Sign-on for any users of the mobile app.
- D. Use Google Authenticator as an additional part of the login process.
Answer: B,D
NEW QUESTION 35
Northern Trail Outfitters (NTO) has an existing custom business-to-consumer (B2C) website that does NOT support single sign-on standards, such as Security Assertion Markup Language (SAMi) or OAuth. NTO wants to use Salesforce Identity to register and authenticate new customers on the website.
Which two Salesforce features should an identity architect use in order to provide username/password authentication for the website?
Choose 2 answers
- A. Delegated Authentication
- B. Connected Apps
- C. Identity Connect
- D. Embedded Login
Answer: A,D
NEW QUESTION 36
After a recent audit, universal containers was advised to implement Two-factor Authentication for all of their critical systems, including salesforce. Which two actions should UC consider to meet this requirement? Choose 2 answers
- A. Require users to provide their RSA token along with their credentials.
- B. Require users to enter a second password after the first Authentication
- C. Require users to supply their email and phone number, which gets validated.
- D. Require users to use a biometric reader as well as their password
Answer: A,D
NEW QUESTION 37
A financial services company uses Salesforce and has a compliance requirement to track information about devices from which users log in. Also, a Salesforce Security Administrator needs to have the ability to revoke the device from which users log in.
What should be used to fulfill this requirement?
- A. Use the Activations feature to meet the compliance requirement to track device information.
- B. Use Login Flows to capture device from which users log in and store device and user information in a custom object.
- C. Use the Login History object to track information about devices from which users log in.
- D. Use multi-factor authentication (MFA) to meet the compliance requirement to track device information.
Answer: A
NEW QUESTION 38
Universal containers (UC) has an e-commerce website while customers can buy products, make payments, and manage their accounts. UC decides to build a customer Community on Salesforce and wants to allow the customers to access the community for their accounts without logging in again. UC decides to implement ansp-Initiated SSO using a SAML-BASED complaint IDP. In this scenario where salesforce is the service provider, which two activities must be performed in salesforce to make sp-Initiated SSO work? Choose 2 answers
- A. Create a connected App
- B. Configure SAML SSO settings.
- C. Set up my domain
- D. Configure Delegated Authentication
Answer: B,C
NEW QUESTION 39
Universal Containers (UC) would liketo enable self-registration for their Salesforce Partner Community Users.
UC wants to capture some custom data elements from the partner user, and based on these data elements, wants to assign the appropriate Profile and Account values.
Which two actions should the Architect recommend to UC1
Choose 2 answers
- A. Modify the CommunitiesSelfRegController to assign theProfile and Account.
- B. Configure Registration for Communities to use a custom Visualforce Page.
- C. Modify the SelfRegistration trigger to assign Profile and Account.
- D. Configure Registration for Communities to use a custom Apex Controller.
Answer: A,B
NEW QUESTION 40
Universal Containers (UC) would like to enable self-registration for their Salesforce Partner Community Users. UC wants to capture some custom data elements from the partner user, and based on these data elements, wants to assign the appropriate Profile and Account values.
Which two actions should the Architect recommend to UC1
Choose 2 answers
- A. Modify the CommunitiesSelfRegController to assign the Profile and Account.
- B. Configure Registration for Communities to use a custom Visualforce Page.
- C. Modify the SelfRegistration trigger to assign Profile and Account.
- D. Configure Registration for Communities to use a custom Apex Controller.
Answer: A,B
NEW QUESTION 41
Northern Trail Outfitters would like to automatically create new employee users in Salesforce with an appropriate profile that maps to its Active Directory Department.
How should an identity architect implement this requirement?
- A. Use the updateUser method in the Just-in-Time (JIT) provisioning registration handler to assign the appropriate profile.
- B. Use a login flow to collect Security Assertion Markup Language attributes and assign the appropriate profile during Just-In-Time (JIT) provisioning.
- C. Make a callout during the login flow to query department from Active Directory to assign the appropriate profile.
- D. Use the createUser method in the Just-in-Time (JIT) provisioning registration handler to assign the appropriate profile.
Answer: A
NEW QUESTION 42
Universal Containers (UC) has decided to build a new, highly sensitive application on the Force.com platform.
The security team at UC has decided that they want users to provide a fingerprint in addition to username/password to authenticate to this application. How can an Architect support fingerprints as a form of identification for Salesforce authentication?
- A. Use delegated Authentication with callouts to a third-party fingerprint scanning application.
- B. Use custom login flows with callouts to a third-party fingerprint scanning application.
- C. Use an AppExchange product that does fingerprint scanning with native Salesforce Identity Confirmation.
- D. Use Salesforce Two-factor authentication with callouts to a third-party fingerprint scanning application.
Answer: C
NEW QUESTION 43
A global company has built an external application that uses data from its Salesforce org via an OAuth 2.0 authorization flow. Upon logout, the existing Salesforce OAuth token must be invalidated.
Which action will accomplish this?
- A. Use a HTTP POST to request the refresh token for the current user.
- B. Enable Single Logout with a secure logout URL.
- C. Use a HTTP POST to the System for Cross-domain Identity Management (SCIM) endpoint, including the current OAuth token.
- D. Use a HTTP POST to make a call to the revoke token endpoint.
Answer: D
NEW QUESTION 44
Universal Containers (UC) has implemented SAML-based Single Sign-On to provide seamless access to its Salesforce Orgs, financial system, and CPQ system. Below is the SSO implementation landscape.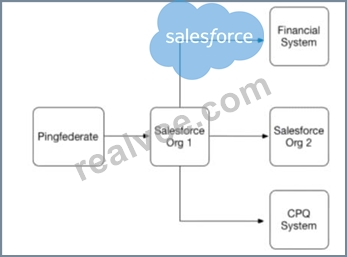
What role combination is represented by the systems in this scenario''
- A. Salesforce Org1 and Salesforce Org2 are acting as Identity Providers.
- B. Salesforce Org1 and PingFederate are acting as Identity Providers.
- C. Financial System and CPQ System are the only Service Providers.
- D. Salesforce Org1 and Salesforce Org2 are the only Service Providers.
Answer: B
NEW QUESTION 45
Universal Containers (UC) is looking to purchase a third-party application as an Identity Provider. UC is looking to develop a business case for the purchase in general and has enlisted an Architect for advice. Which two capabilities of an Identity Provider should the Architect detail to help strengthen the business case? Choose 2 answers
- A. The Identity Provider can authenticate multiple applications.
- B. The Identity provider can store credentials for multiple applications.
- C. The Identity Provider can authenticate multiple social media accounts.
- D. The Identity Provider can centralize enterprise password policy.
Answer: A,D
NEW QUESTION 46
What is one of the roles of an Identity Provider in a Single Sign-on setup using SAML?
- A. Create token
- B. Revoke token
- C. Consume token
- D. Validate token
Answer: A
NEW QUESTION 47
universal containers wants to build a custom mobile app connecting to salesforce using Oauth, and would like to restrict the types of resources mobile users can access. What Oauth feature of Salesforce should be used to achieve the goal?
- A. Access Tokens
- B. Scopes
- C. Refresh Tokens
- D. Mobile PINS
Answer: A
NEW QUESTION 48
......
What is the duration of the Identity-and-Access-Management-Designer Exam
- Passing Score: 65%
- Number of Questions: 60
- Format: Multiple choices, multiple answers
- Length of Examination: 120 minutes
Certification Path
There is no prerequisite for this exam.
Identity-and-Access-Management-Designer Deluxe Study Guide with Online Test Engine: https://www.realvce.com/Identity-and-Access-Management-Designer_free-dumps.html
NEW 2022 Certification Sample Questions Identity-and-Access-Management-Designer Dumps & Practice Exam: https://drive.google.com/open?id=1-jfIzdpb9EbYBNbDLgSuo1ZdZXkwJ5wS